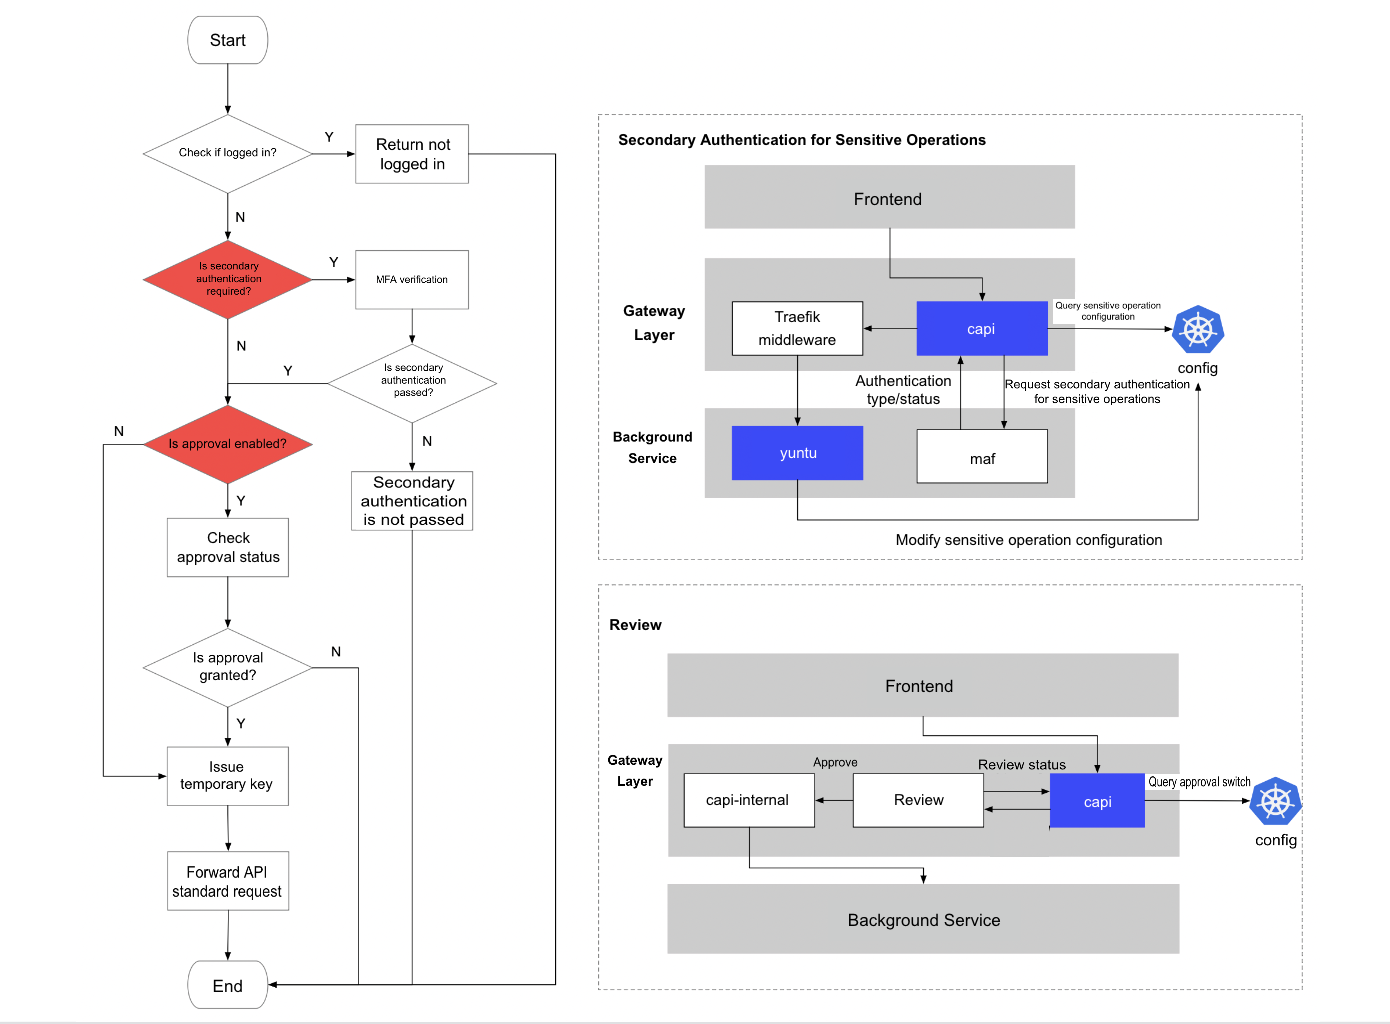
The core process of capi in controlling cloud API requests is as follows:
- Login check process: Based on the UIN and SKey, the system requests the authentication service to verify the login status.
- Secondary authentication process for sensitive operations: The gateway checks whether the API is a sensitive operation and whether secondary authentication is enabled. If the secondary authentication is enabled, it returns a special error code to the frontend. The frontend pops up a window prompting the user to enter a code and resubmit the request. The gateway passes through the code to MFA for verification.
- Approval check process:
- The gateway checks whether the approval switch is enabled. If the switch is enabled, it calls the approval service to create an approval record. Subsequent requests will call the approval service to check whether the approval status is passed.
- If the approval passes, it will call capi-internal to simulate a frontend request to the gateway to make the request take effect.