Type Overview
Converge Cloud provides two types of cloud WAF, SaaS WAF and CLB WAF. The security protection capabilities provided by the two WAFs are basically the same, but the access methods and applicable scenarios are different. You can choose the appropriate type of WAF according to your actual deployment needs.
| Category | SaaS Type | CLB Type |
|---|---|---|
| Applicable scenario | Applicable to all users (cloud users or local IDC users). Domain name access is achieved through DNS resolution scheduling. | Applicable to users who have used or plan to use layer-7 CLB on Converge Cloud. |
| Core strengths | ·It has a broad scope of application, covering users both on Converge Cloud and not on Converge Cloud. ·It supports hiding the origin server to reduce the exposure surface of risks. |
·It features seamless access and millisecond-level latency. The existing network architecture does not need to be adjusted for WAF access. ·It features separate website workload forwarding and security protection, with one-click bypass to ensure the security, stability, and reliability of the website workload. ·It supports multi-region access. |
| How to choose | For users who have websites that need protection both on Converge Cloud and locally, or do not use layer-7 CLB on Converge Cloud, it is recommended to use SaaS WAF. | For users who have used or plan to use layer-7 CLB on Converge Cloud and have the needs of web security protection, compliance protection, and website security operations, it is recommended to use CLB WAF. |
Note:
CLB WAF is currently available in grayscale. If you need to use it, submit an application, and we will verify and activate it for you as soon as possible.
SaaS WAF
WAF is delivered in a SaaS model. By modifying the DNS traffic diversion settings, web protection capabilities can be obtained in minutes on the user side without the need to deploy any hardware equipment. After the WAF cluster performs malicious traffic detection and protection on the protected domain names, it performs the origin-pull operation on normal traffic to the origin server to protect website security.
CLB WAF
WAF integrates with the layer-7 CLB (listener) cluster in various network environments of Converge Cloud through domain name configuration to perform bypass threat detection and filtering on HTTP/HTTPS traffic transiting through the CLB, realize the separation of workload forwarding and security protection, minimize the impact of security protection on the network workload, and protect stable website operation.
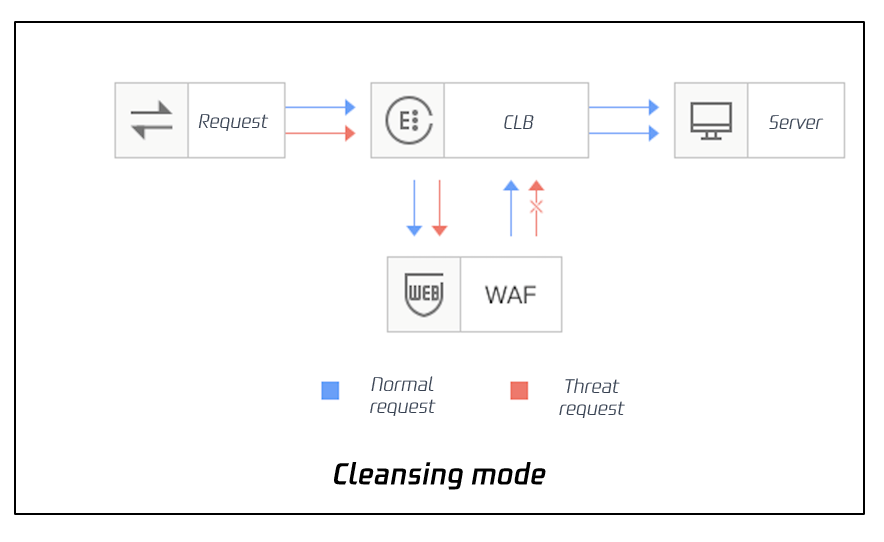
CLB WAF provides two traffic processing modes:
- Mirror mode: Associated with WAF through a domain name, CLB mirrors traffic to the WAF cluster, which performs bypass detection and alarming but does not return the request credibility status.
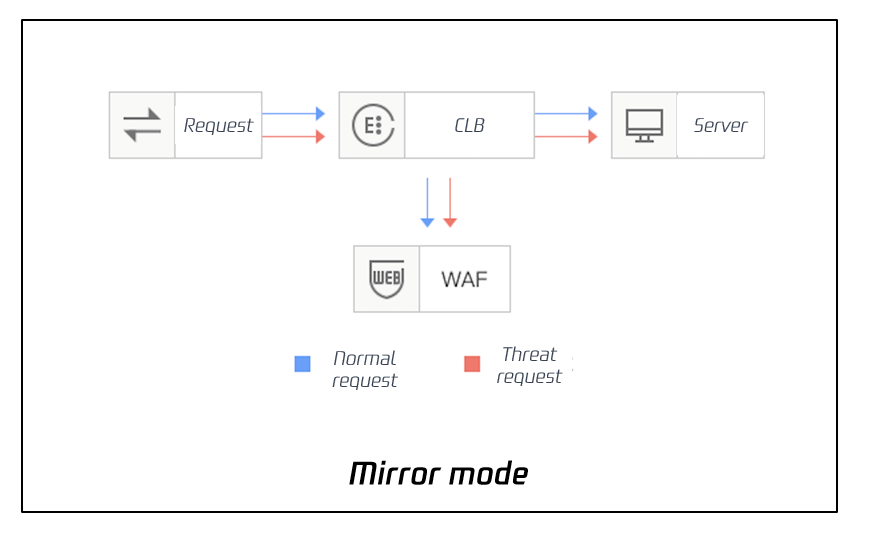
- Cleansing mode: Associated with WAF through a domain name, CLB mirrors traffic to the WAF cluster, which performs bypass detection and alarming and synchronizes the request credibility status. Then, the CLB cluster will block or allow the requests based on their status.