

This document describes how to perform rule protection settings through WAF to protect against web attacks.
Background Information
WAF uses a rule protection engine based on regular expressions and an AI protection engine based on machine learning to protect against web vulnerabilities and unknown threats.
The WAF rule protection engine provides expert rule sets based on our accumulated web threat intelligence to prevent OWASP top 10 attacks. Currently, it can defend against 12 categories of common web attacks, such as SQL injections, XSS attacks, malicious scans, command injection attacks, web application vulnerabilities, WebShell uploads, non-compliant protocols, Trojans, and backdoors.
The WAF rule protection engine supports rule level configuration. You can configure the rule protection level according to your actual business needs, and enable or disable rule sets, individual rules, and preset rules. You can also use the allowlist of specified URLs and rule IDs to process false positives.
Operation Steps
Settings of Domain Name Rule Protection Engine
- Log in to the WAF console. In the left sidebar, select Configuration Center > Basic Security > WEB Security.
- On the protection settings page, configure the protection mode, protection level, and malicious file detection method for basic web protection. On this page, you can also enable the scan protection feature and set IP address blocking rules.
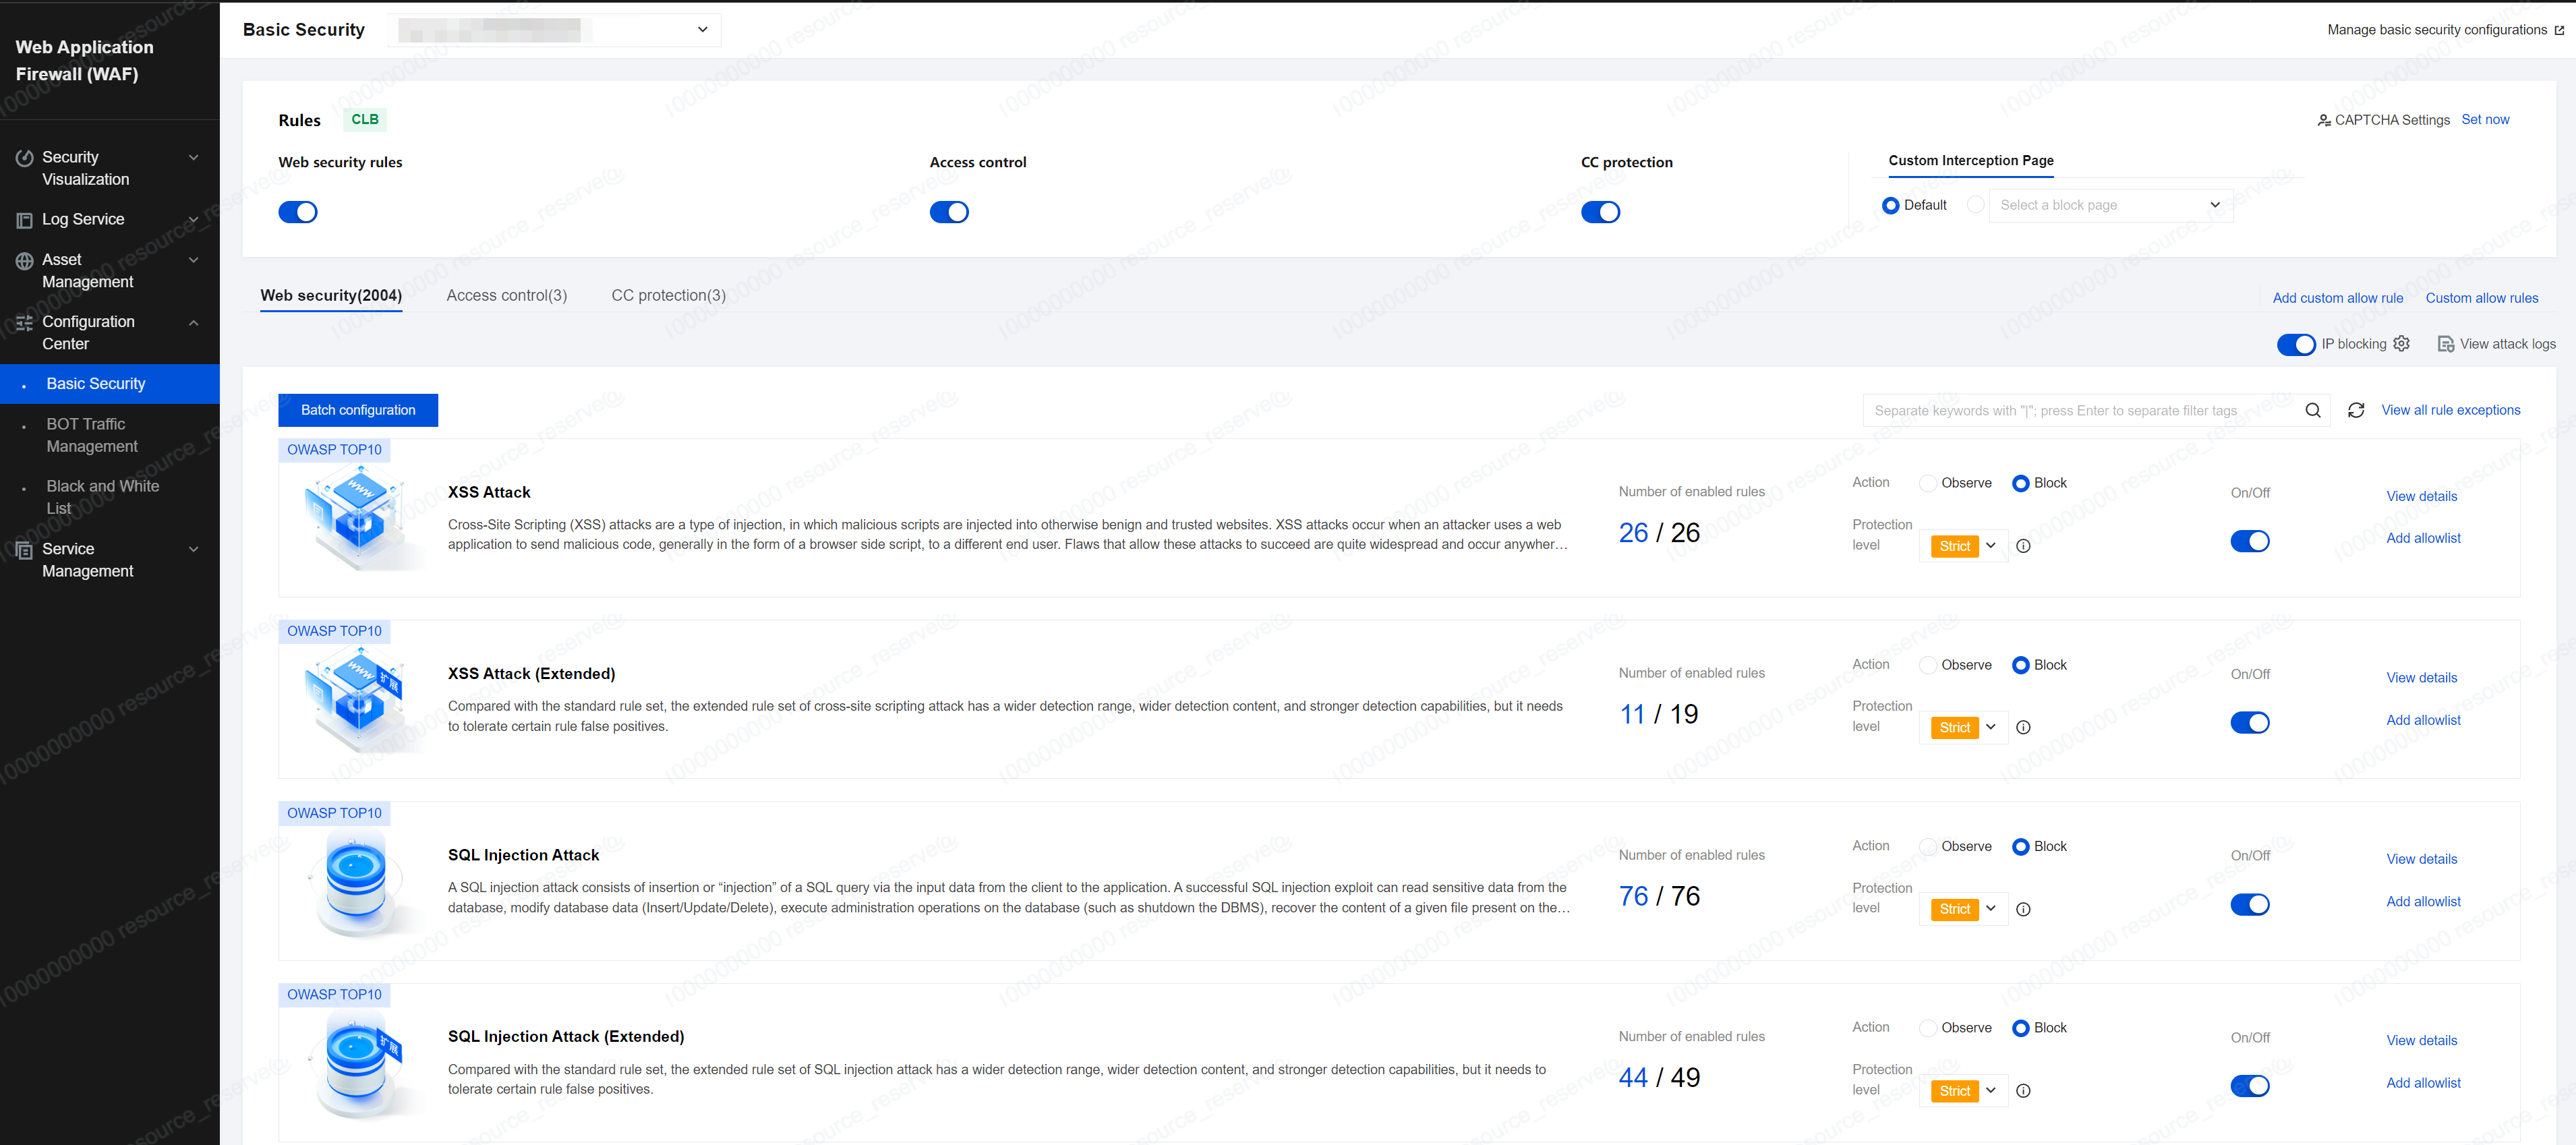
Field description:
- Rule Engine Switch: The switch is turned on by default. When it is turned off, requests for domain names passing through WAF will not undergo threat processing by the rule engine.
- Protection Mode: Rule engine operation mode, which is set to Interception by default.
- Observation: Does not block attack requests, but triggers alarms and generates observation logs.
- Interception: Directly blocks web attack requests and generates interception logs.
- Protection level: Rule engine protection level, which is normal by default.
- Normal: detects common web application attacks. If you notice excessive false interceptions at the default level, or if your workload involves significant uncontrolled user input (such as websites with rich text editors), it is recommended that you select this mode.
- Strict: strictly detects web application attacks such as SQL injections, XSS attacks, and command execution. It is the default mode.
- Rule management: Through rule management, users can view rule engine information and set the rule engine, including viewing attack classifications, viewing rule content included in rule levels and rule set update dynamics, enabling or disabling single rules, and adding rules to the allowlist based on domain name URLs and rule IDs.
- Supported decoding types: The rule engine currently supports the following decoding types by default and does not support manual configuration.
- URL decoding (multiple decoding), JavaScript Unicode decoding, comment processing, whitespace compression, UTF-7 decoding, HTML entity decoding, Multipart parsing, JSON parsing, XML parsing, and Form parsing.
- Batch configuration: Supports unified default settings for multiple threat types.
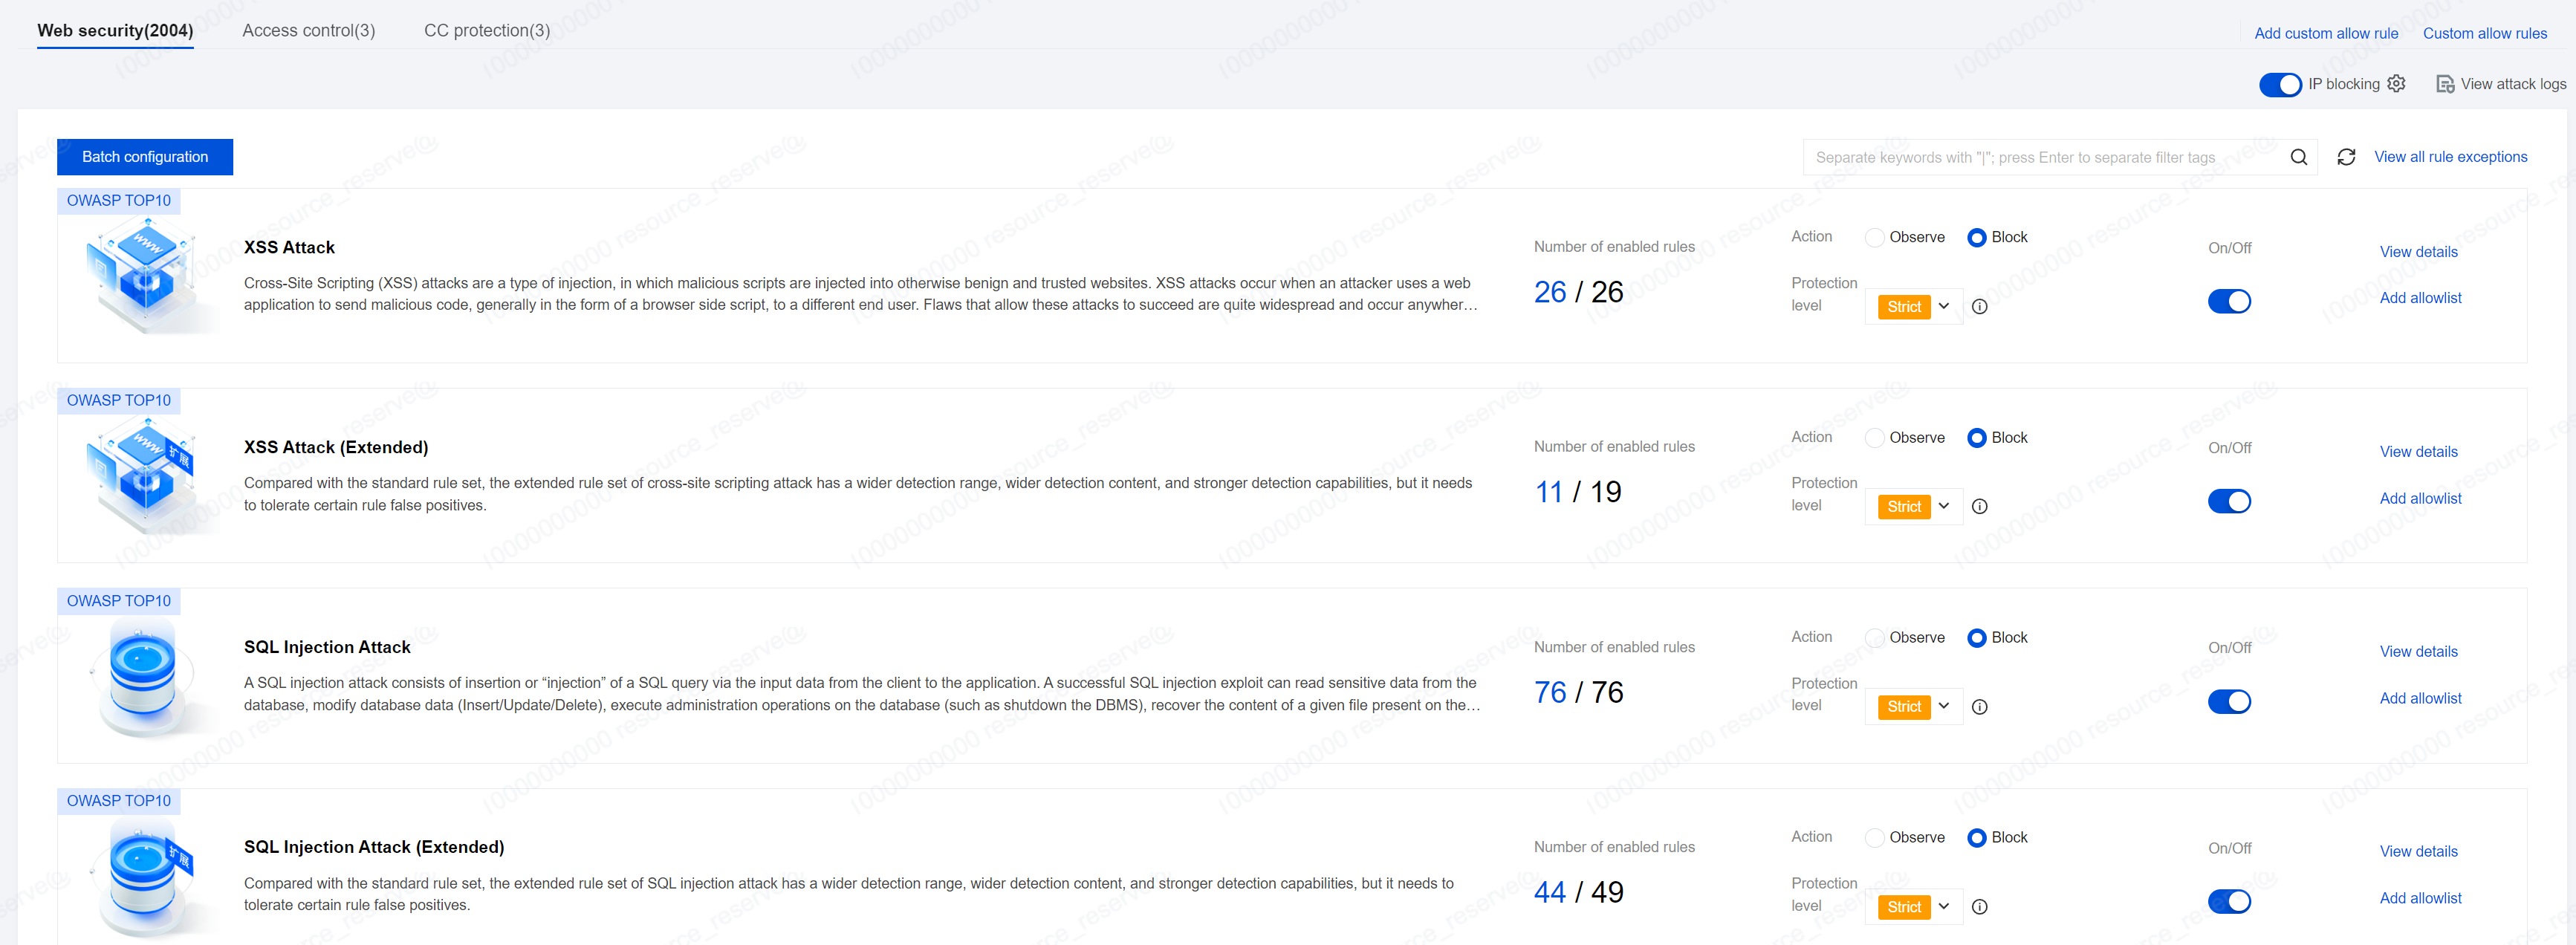
Viewing rule classifications
- Enter the Rule Engine Settings page.
- Method 1: Log in to the WAF console. In the left sidebar, choose Asset Center > Access Management to go the domain name list management page. Select any domain name and click Protection Configuration in the Operation column to go to the web security protection configuration page of the domain name and view rule details.
- Method 2:
- a. Log in to the WAF console. In the left sidebar, choose Configuration Center > Basic Security.
- b. In the domain name list, click the domain name to be protected to go to the web security settings page, and then go to the rule engine page.
- Enter the Rule Base Management page.
Log in to the WAF console. In the left sidebar, choose Service Management > Web Rule Base to view descriptions of attack categories currently protected by WAF and updates on rules.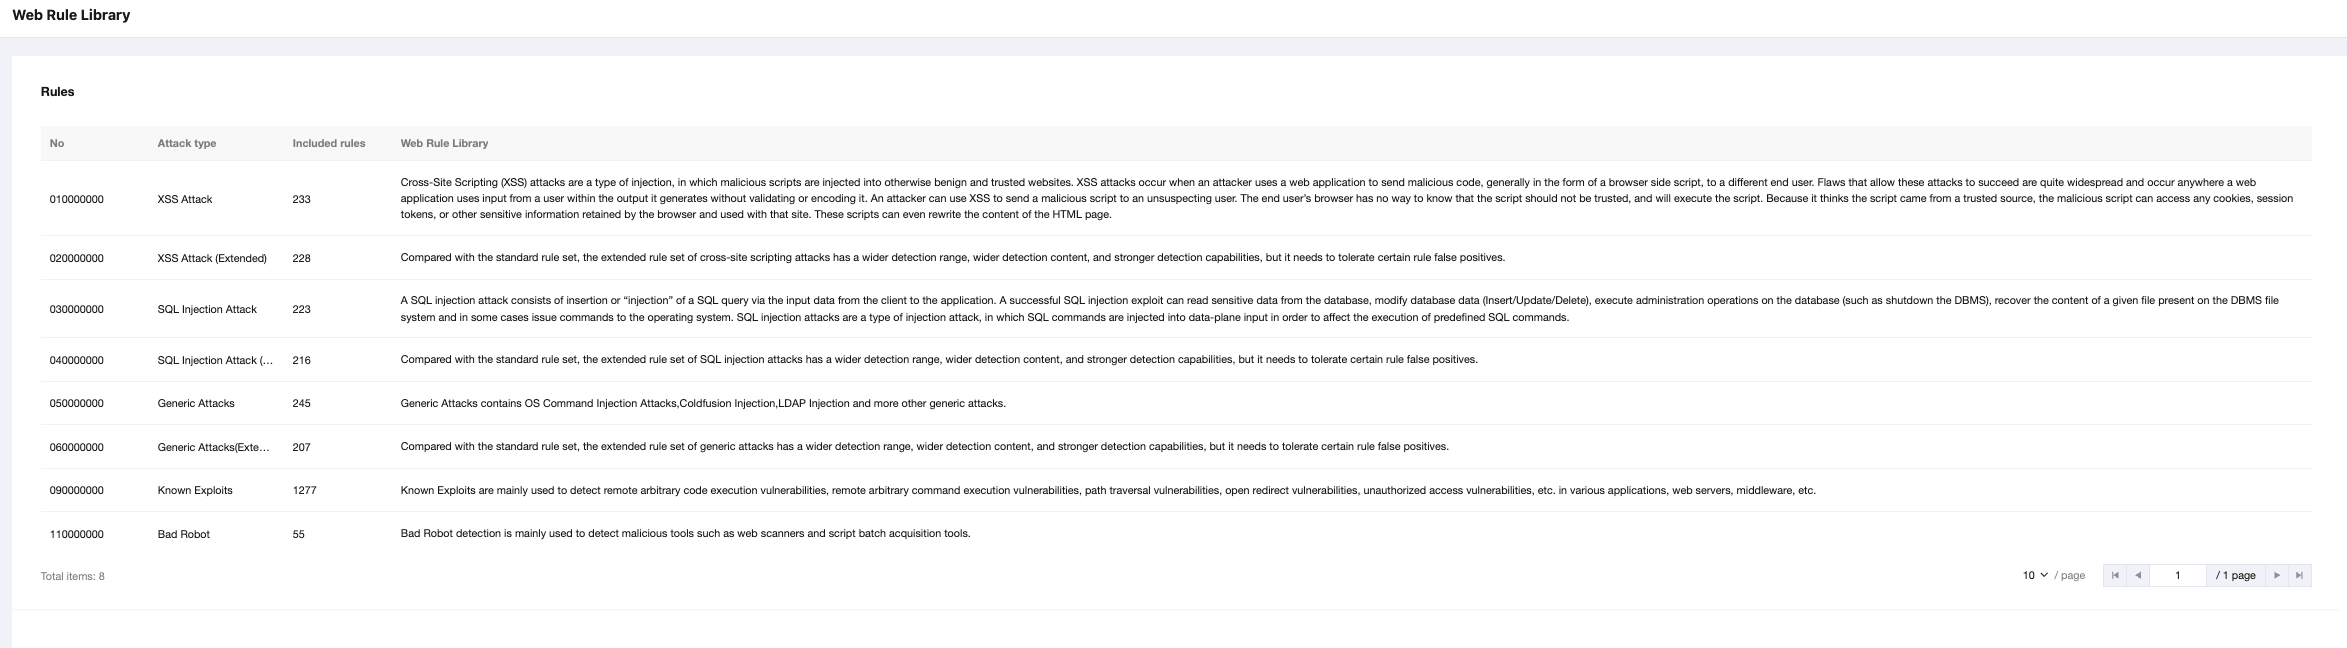
The attack classifications supported by the current WAF for protection are as follows:
| Attack Classification | Attack Description |
|---|---|
| XSS attack | XSS attacks are a type of injection where malicious scripts are injected into other trusted websites. An XSS attack occurs when an attacker uses a web application to send malicious code (typically in the form of a browser-side script) to a different end user. Flaws that allow these attacks to succeed are widespread and occur wherever a web application uses input from a user within its generated output without validating or encoding it. Attackers can use XSS to send malicious scripts to unsuspecting users. The end user's browser has no way of knowing that the script should not be trusted and will execute it. Since it believes the script comes from a trusted source, the malicious script can access any cookies, session tokens, or other sensitive information retained by the browser and used with that site. These scripts can even rewrite the content of HTML pages. |
| XSS attack (extended) | The extended rule set of XSS attacks has a broader detection range, wider detection content, and stronger detection capability compared with the standard rule set, but it needs to tolerate certain rule false positives. |
| SQL injection attack | SQL injection attacks include inserting or "injecting" SQL queries through input data from the client to the application. A successful SQL injection vulnerability can read sensitive data from the database, modify (insert/update/delete) database data, perform management operations on the database (such as shutting down the DBMS), recover the content of a given file existing in the DBMS file, and issue a command to the operating system in some cases. The SQL injection attack is a type of injection attack where SQL commands are injected into data plane inputs to impact the execution of predefined SQL commands. |
| SQL injection attack (extended) | The extended rule set for SQL injection attacks has a broader detection range, wider detection content, and stronger detection capabilities compared to the standard rule set, but requires tolerance for a certain degree of rule false positives. |
| General attack | General attacks include operating system command injection attacks, Coldfusion injections, LDAP Injections, and other general attacks. |
| General attack (extended) | The extended rule set of general attacks has a broader detection range, wider detection content, and stronger detection capability compared with the standard rule set, but it needs to tolerate certain rule false positives. |
| Known weakness | Known weaknesses are primarily used to detect various remote code execution vulnerabilities, remote command execution vulnerabilities, path traversal vulnerabilities, open redirect vulnerabilities, and unauthorized access vulnerabilities occurring in applications, web servers, and middleware. |
| Bad bot | Bad bot detection is primarily used to detect malicious tools such as web scanners and batch script obtaining tools. |
Rule management
- Log in to the WAF console. In the left sidebar, choose Configuration Center > Basic Security, select the domain name to be managed, and then go to the web security page.
- On the web security management page, enable or disable rules, set Protection Mode to Observation, and add rules to the allowlist.
Remarks: The interception mode is enabled for all rules by default.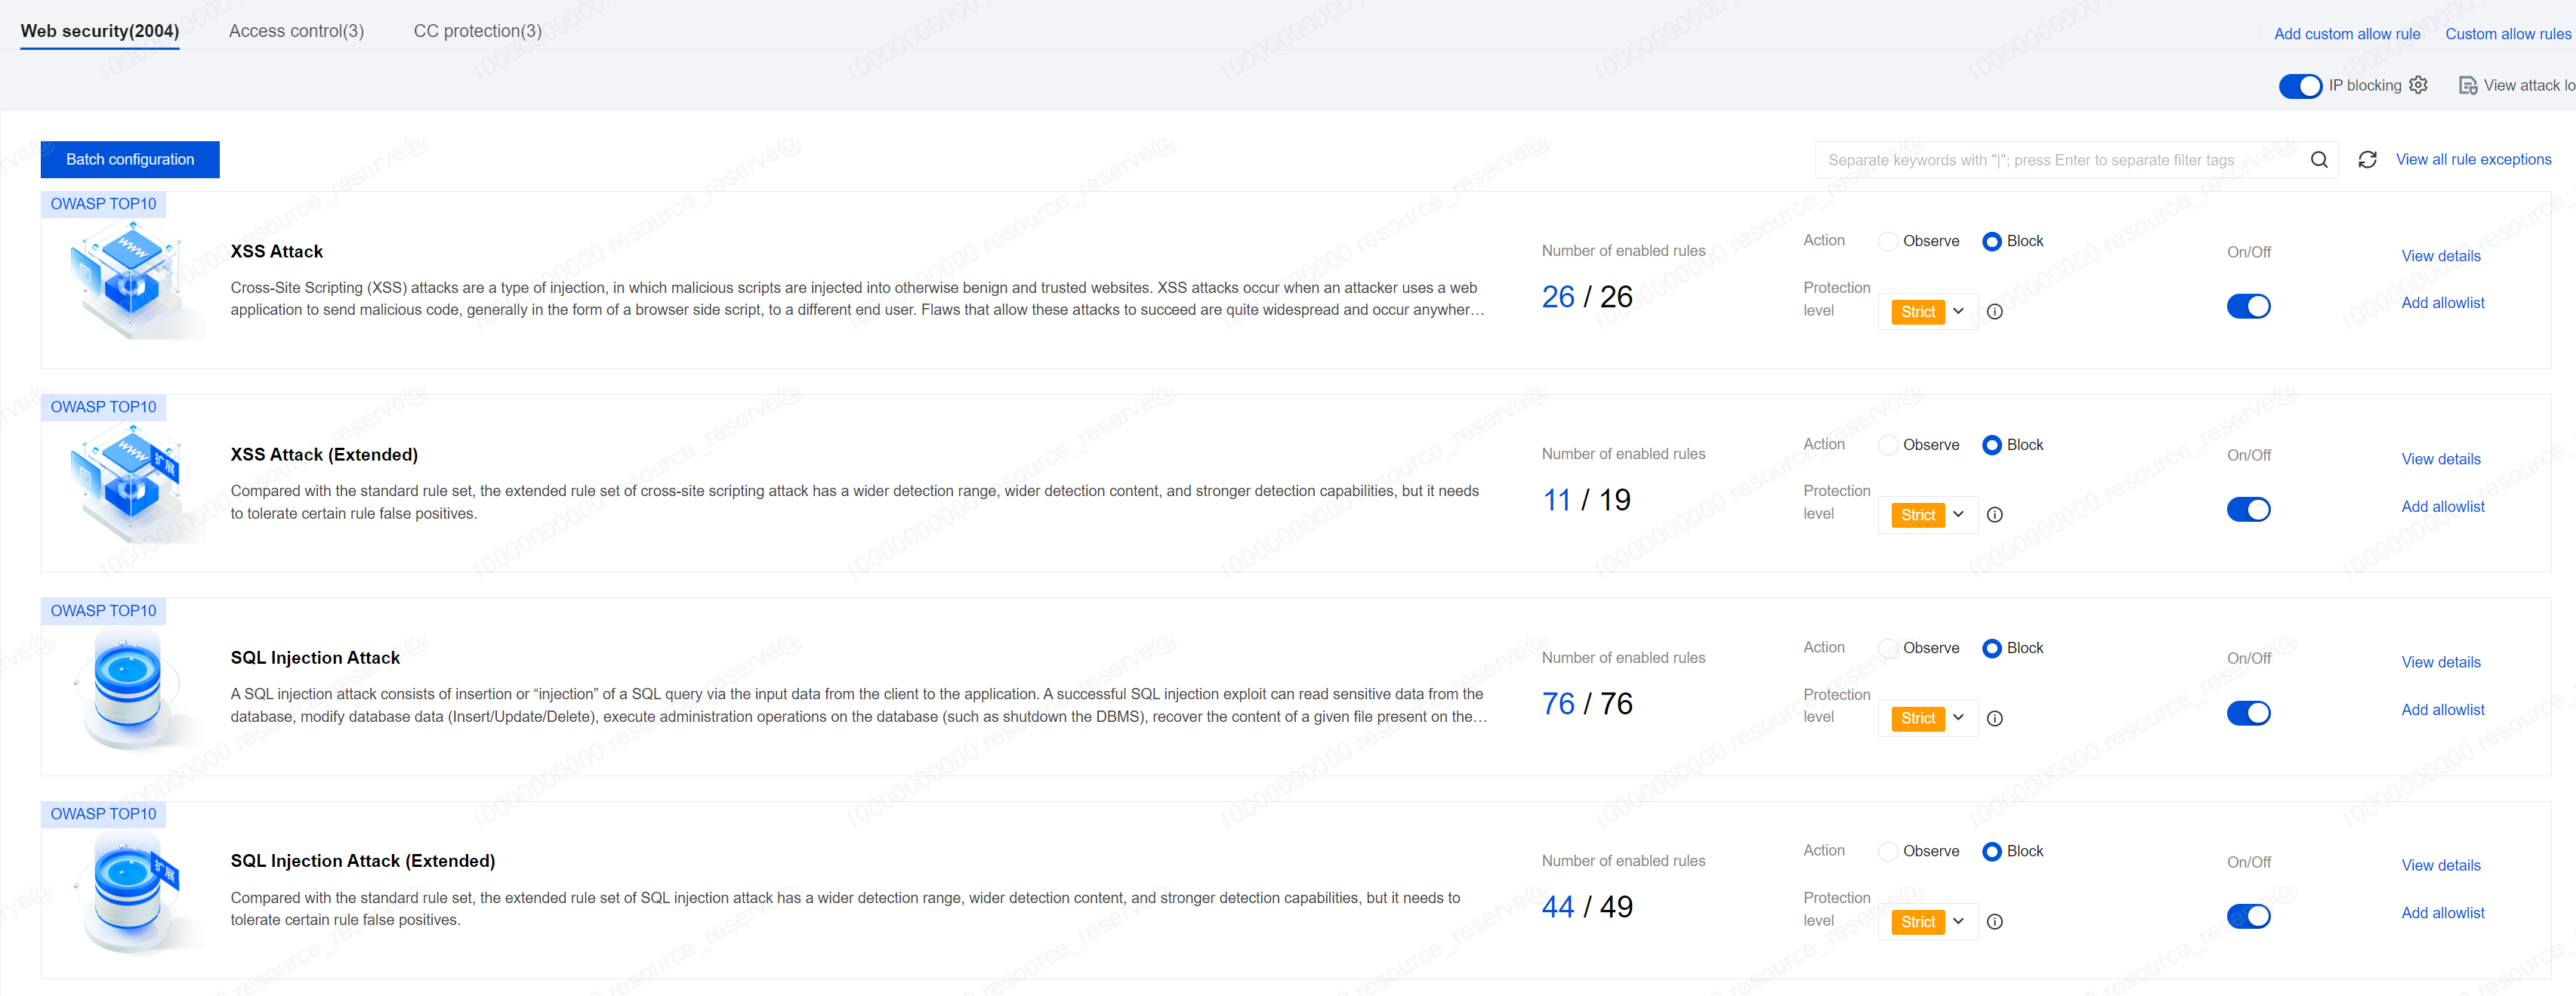
- Users can search for rule sets according to Rule Level, Attack Classification, and CVEID, or by entering Rule ID, and view specific rules and perform operations.
Note:
The strict rule level includes normal and strict rules.
